
The Lead Cybersecurity Manager training course enables participants to obtain the necessary competencies to effectively implement, manage, and continually improve a cybersecurity program.
Learning Objectives
Upon successfully completing the training course, participants will be able to:
- Explain the fundamental concepts, strategies, methodologies, and techniques employed to implement and manage a cybersecurity program
- Explain the relationship between ISO/IEC 27032, NIST Cybersecurity Framework, and other relevant standards and frameworks
- Comprehend the operation of a cybersecurity program and its components
- Support an organization in operating, maintaining, and continually improving their cybersecurity program
Why should you attend?
Organizations nowadays are affected by the ever-evolving digital landscape and constantly face new threats and complex and sophisticated cyberattacks. There is a pressing need for skilled individuals capable of effectively managing and implementing robust cybersecurity programs to counter these threats. Our Lead Cybersecurity Manager training course has been developed to address this need.
By attending the PECB Certified Lead Cybersecurity Manager, participants will learn the fundamental cybersecurity concepts, strategies, methodologies, and techniques utilized to effectively establish and manage a cybersecurity program based on the guidance of international standards for cybersecurity, such as ISO/IEC 27032 and the NIST Cybersecurity Framework. Additionally, this training course empowers participants to enhance their organization’s readiness and resilience against cyber threats. Participants will be well-prepared to support their organization’s ongoing cybersecurity efforts and make valuable contributions in today’s ever-evolving cybersecurity landscape.
Who should attend?
This training course is intended for:
- Managers and leaders involved in cybersecurity management
- Individuals tasked with the practical implementation of cybersecurity strategies and measures
- IT and security professionals seeking to advance their careers and contribute more effectively to cybersecurity efforts
- Professionals responsible for managing cybersecurity risk and compliance within organizations
- C-suite executives playing a crucial role in decision-making processes related to cybersecurity
Educational Approach
- The training course covers theoretical concepts and practical examples in cybersecurity, enabling participants to grasp the effective application of cybersecurity strategies and technologies.
- The training course includes various assessments, including essay-type exercises, and multiple-choice quizzes, some of which are scenario-based.
- The participants are encouraged to interact and have meaningful discussions with each other while working on quizzes and exercises, creating a collaborative learning environment.
- The quiz structure within the course closely mirrors that of the certification exam, ensuring participants are well-prepared for the exam
Prerequisites
To fully benefit from this training course, participants should have a fundamental understanding of cybersecurity concepts and management.
Training Course Structure
Introduction to cybersecurity and initiation of a cybersecurity program implementation
- Training course objectives and structure
- Standards and regulatory frameworks
- Fundamental concepts of cybersecurity
- Cybersecurity program
- The organization and its context
- Cybersecurity governance
Cybersecurity roles and responsibilities, risk management, and attack mechanisms
- Cybersecurity roles and responsibilities
- Asset management
- Risk management
- Attack mechanisms
Cybersecurity controls, communication, and awareness and training
- Cybersecurity controls
- Cybersecurity communication
- Awareness and training
Cybersecurity incident management, monitoring, and continual improvement
- ICT readiness in business continuity
- Cybersecurity incident management
- Testing in cybersecurity
- Measuring and reporting cybersecurity performance and metrics
- Continual improvement
- Closing of the training course
Certification Exam
- Exam Duration : 3 hours
Examination
The “PECB Certified Lead Cybersecurity Manager” exam fully meets all the requirements of the PECB Examination and Certification Program (ECP). It covers the following competency domains:
- Domain 1: Fundamental concepts of cybersecurity
- Domain 2: Initiating the cybersecurity program and cybersecurity governance
- Domain 3: Defining cybersecurity roles and responsibilities and managing risks
- Domain 4: Selecting cybersecurity controls
- Domain 5: Establishing cybersecurity communication and training programs
- Domain 6: Integrating the cybersecurity program in business continuity management and incident management
- Domain 7: Measuring the performance of and continually improving the cybersecurity program
For specific information about the exam type, languages available, and other details, please visit the List of PECB Exams and Exam Rules and Policies.
Certification
After passing the exam, you can apply for one of the credentials shown on the table below. You will receive a certificate once you fulfill all the requirements of the selected credential.
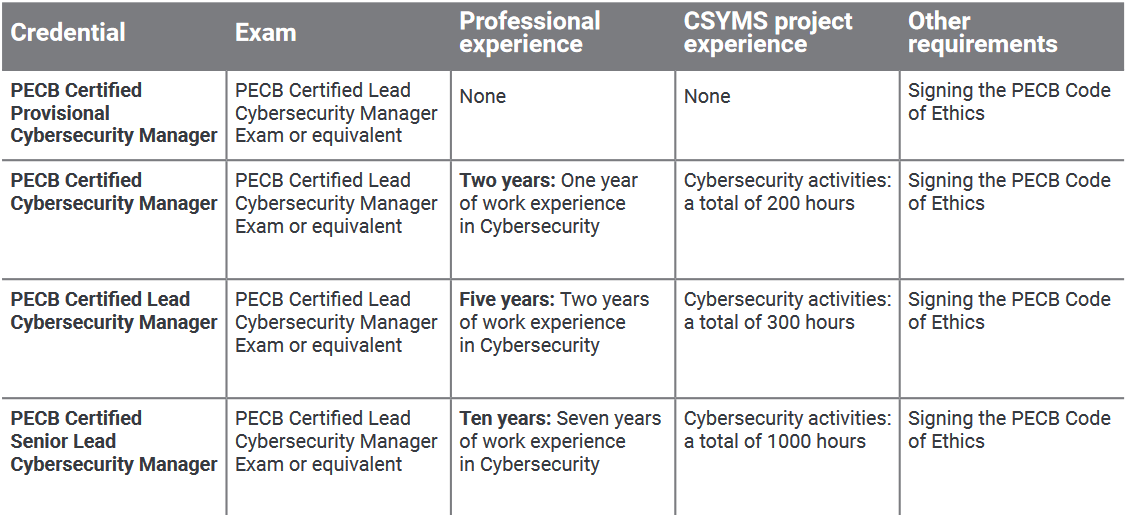
PECB Certified Lead Cybersecurity Manager
The cybersecurity management activities should follow best practices and include the following:
- Conducting a gap analysis on the cybersecurity program
- Developing a cybersecurity policy
- Assessing and treating cybersecurity risks
- Implementing cybersecurity controls
- Measuring and reporting cybersecurity performance and metrics
For more information about cybersecurity certifications and the PECB Certification process, please refer to Certification Rules and Policies.