
The Lead SOC 2 Analyst training course equips participants with the knowledge and skills necessary to support organizations in establishing and implementing security measures based on the SOC 2 requirements. These requirements are established by the American Institute of Certified Public Accountants (AICPA), specifying how service organizations should handle sensitive customer data based on five trust security services: security, availability, integrity, confidentiality, and privacy. In addition to earning proficiency in SOC 2, participants will also learn about the role of key stakeholders and the importance of working with other organizations to ensure effective compliance management and possess the necessary competencies to manage a SOC 2 implementation team.
Learning Objectives
By the end of this training course, you will be able to:
- Explain the fundamental concepts and principles of the SOC 2 framework
- Interpret the SOC 2 requirements from an analytical perspective
- Initiate and plan the implementation of security measures based on SOC 2 requirements by utilizing PECB’s methodology and other best practices
- Support an organization in operating, maintaining, and continually improving security measures based on SOC 2 requirements
- Prepare an organization to undergo a SOC 2 certification audit
Why should you attend?
In current the digital age, information security is a critical concern for most industries. SOC 2 compliance is crucial for organizations handling sensitive data and outsourcing key business operations. SOC 2 compliance demonstrates a commitment to data security and privacy. This training course equips participants with the skills to manage and mitigate information security risks, align with regulatory requirements, and build trust with clients and stakeholders.
Upon passing the exam, participants can apply for the “PECB Certified Lead SOC 2 Analyst” credential, showcasing their proficiency in effectively managing SOC 2 compliance and enhancing their ability to ensure the integrity and security of their organization’s information systems.
Who should attend?
This training course is intended for:
- Managers or consultants seeking to expand their knowledge of SOC 2 compliance and controls
- IT professionals and information security risk managers seeking to enhance their expertise in SOC 2 requirements and best practices
- Compliance officers responsible for establishing, implementing, and managing SOC 2 compliance programs within their organizations
- Members of audit and compliance teams involved in SOC 2 readiness assessments and internal audits
- Professionals seeking to establish and manage effective information security and compliance controls that meet SOC 2 criteria
- Executives and business leaders who must comprehend SOC 2 compliance to assist their company’s risk management and compliance programs
- Security analysts and incident response coordinators tasked with ensuring the security, availability, processing integrity, confidentiality, and privacy of information systems
Educational Approach
- This training course combines theoretical concepts with best practices for implementing the SOC 2 framework.
- The training course contains essay-type exercises and multiple-choice quizzes, some of which are scenario-based.
- The quiz format closely mirrors that of the certification exam, ensuring participants are well-prepared for the exam.
Prerequisites
The main requirement for participating in this training is having general knowledge of information security practices, information systems and their security controls, compliance standards, and SOC 2 principles
Course Agenda
Introduction to the SOC 2 framework
- Training course objectives and structure
- Introduction to information security standards and regulations
- Overview of the SOC 2 framework
- Trust Services Criteria (TSC)
- Initiation of the SOC 2 compliance program
- Analysis of the SOC 2 compliance requirements
- Defining the SOC 2 scope
Risk management and policy development
- Gap analysis and remediation
- Risk management
- Documentation requirements and policy development
- Roles and responsibilities
- Implementation of controls
Implementing SOC 2 controls and incident response
- Implementation of controls (cont’d)
- Incident management and BCDR
- Awareness and training
Auditing, reporting, and continual improvement
- SOC 2 audit readiness and analysis
- Monitoring and reporting
- Continual improvement
- Closing of the training course
Certification Exam
- 3 Hours Exam
Examination
The “PECB Certified Lead SOC 2 Analyst” exam meets the PECB Examination and Certification Program (ECP) requirements. It covers the following competency domains:
- Domain 1: Fundamental principles and concepts of SOC 2 Framework
- Domain 2: SOC 2 criteria
- Domain 3: Planning of SOC 2 requirements implementation
- Domain 4: Implementation of SOC 2 requirements
- Domain 5: Monitoring of security measures and preparing for SOC 2 certification audit
For specific information about the exam type, languages available, and other details, please visit the List of PECB Exams and Exam Rules and Policies.
Certification
After successfully passing the exam, you can apply for one of the credentials shown on the table below. You will receive a certification once you fulfill all the requirements of the selected credential.
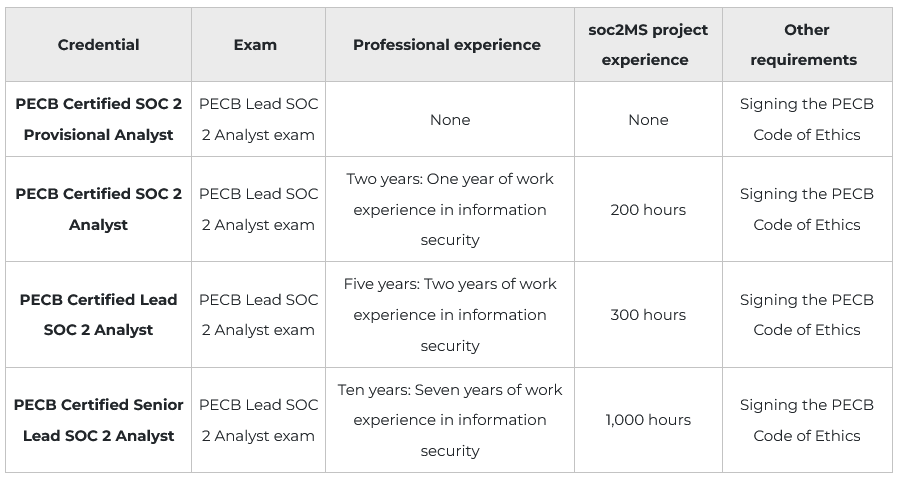
Lead SOC 2 Analyst Systems and Organization Controls
The SOC 2 project experience should follow best implementation practices and include the following:
- Conducting a gap analysis on a SOC 2 program
- Developing an information security policy
- Assessing and treating information security risks
- Implementing SOC 2 controls
- Measuring and reporting SOC 2 performance and metrics
For more information about SOC 2 certifications and the PECB Certification process, please refer to Certification Rules and Policies.
What is SOC 2?
In the modern world, SOC 2, which stands for Systems and Organization Controls, has become a crucial framework for assessing data controls, security, and privacy based on established Trust Service Criteria. This framework assists organizations in managing risks, increasing confidence among customer and partners, differentiating themselves from competitors, and improving security measures for other compliance models. Essential for its role in verifying an organization’s commitment to protecting the privacy of customer data, SOC 2 specifies stringent measures to counter internal and external threats. SOC 2 compliance is crucial as data breaches can result in significant financial losses and severely damage an organization’s reputation and consumer trust.
SOC 2 audit reports provide detailed evaluations of an organization’s internal controls related to security, availability, processing integrity, confidentiality, and privacy of customer data and are divided into two types:
- SOC 2 Type 1 report: evaluates the design and implementation of a service organization’s controls at a specific point in time, providing assurance of data security and compliance with Trust Service Criteria, which can enhance competitiveness and meet increasing customer demands for data protection.
- SOC 2 Type 2 report: provides higher assurance than SOC 2 Type 1 by thoroughly examining a company’s internal control policies over a specified period of time, demonstrating best practices in data security and control systems, and making the service provider more attractive to potential customers despite the significant investment required.
Benefits of a PECB Lead SOC 2 Analyst certification
A PECB Lead SOC 2 Analyst certificate demonstrates that you can:
- Assess and manage IT system’s security, availability, processing integrity, confidentiality, and privacy
- Assign and manage roles and responsibilities to ensure effective coordination
- Conduct detailed assessments and audits of incident response and risk management capabilities to identify weaknesses and provide actionable recommendations
- Maintain and improve SOC 2 compliance by systematically reviewing and updating security measures and documenting continual improvement activities
- Enable an organization to effectively prepare for and successfully undergo a SOC 2 certification audit
- Achieve professional recognition by completing specific modules, earning CPD credits, and maintaining certification through ongoing professional development activities
For more information, visit the PECB PECB Certified Lead SOC 2 Analyst | Systems and Organization Controls
Download the brochure PECB Certified Lead SOC 2 Analyst | Systems and Organization Controls