

Experiencing security issues is usually not a matter of if but when. Organizations are continuously facing security risks that seriously threaten their operations. High-value products are prone to theft, confidential information is prone to hacking, and personnel are prone to injury. Such security incidents will not only cause financial and business losses, but may also lead to legal consequences and reputational damage. This is why security management has become a crucial aspect for organizations. In this regard, ISO 28000 provides organizations with a comprehensive approach to security management.
Learning Objectives
By the end of this training course, the participants will be able to:
- Explain the fundamental concepts and principles of security management
- Interpret the requirements of ISO 28000 requirements for an SeMS from the perspective of an implementer
- Initiate and plan the implementation of an SeMS based on ISO 28000 by utilizing PECB’s IMS2 Methodology and other best practices
- Support organizations in operating, maintaining, and continually improving their SeMS based on ISO 28000
- Prepare organizations to undergo a third-party certification audit
Why should you attend?
In today’s rapidly evolving environment, organizations face significant security challenges to protect their assets, operations, and reputation. The ever-changing security risks can pose serious threats to organizations; therefore, it is crucial for organizations to establish an effective security management system.
The PECB ISO 28000 Lead Implementer training course helps you develop the necessary competencies to establish, implement, maintain, and continually improve a security management system (SeMS). This training course aims to equip you with an in-depth knowledge of ISO 28000 requirements, as well as the best practices and approaches to security management.
After successfully completing the training course, you will be able to help organizations establish appropriate security processes and controls that proactively ensure the security of the environment and contribute to the creation and protection of value.
After completing the training course, you can sit for the exam. If you pass the exam, you can apply for the “PECB Certified ISO 28000 Lead Implementer” credential. The internationally recognized “PECB Certified ISO 28000 Lead Implementer” certificate demonstrates that you possess the professional capabilities to implement security management systems based on the requirements of ISO 28000.
Who should attend?
- Individuals responsible for maintaining and improving the security environment in which organizations operate
- Professionals wishing to obtain in-depth knowledge of the requirements of ISO 28000
- Individuals responsible for maintaining conformity to the ISO 28000 requirements
- Expert advisors seeking to master the implementation of an SeMS
- Members of an SeMS implementation team
- Individuals seeking to pursue a career in security management
- Security management consultants
- Management representatives seeking to master the SeMS implementation process
Educational Approach
This training course is participant centered and it:
- Elaborates theories, approaches, and best practices used in the implementation, maintenance, and continual improvement of a security management system
- Provides theoretical basis supported by practical examples
- Provides quizzes with stand-alone questions (after each section) and scenario-based quizzes (at the end of each day), intended to prepare the participants for the certification exam
Prerequisites
In order to fully benefit from this training course, participants should have a basic knowledge of ISO 28000 requirements. In addition, a general understanding of security management principles and concepts can also facilitate the learning process.
Course Agenda
Introduction to ISO 28000 and initiation of an SeMS implementation
- Training course objectives and structure
- Standards and regulatory frameworks
- Fundamental concepts and principles of security management
- Initiation of the SeMS implementation
- The organization and its context
Implementation plan of an SeMS
- SeMS scope
- Leadership and organizational structure
- Security policy
- Risks, opportunities, and security objectives
- Resources and competence
- Communication and awareness
Implementation of an SeMS
- Documented information
- Operational planning and control
- Risk assessment and treatment
- Security strategies
- Security plans
SeMS monitoring, continual improvement, and preparation for the certification audit
- Monitoring, measurement, analysis, and evaluation
- Internal audit
- Management review
- Treatment of nonconformities
- Continual improvement
- Preparation for the certification audit
- Closing of the training course
Certification Exam
- 3 Hours Exam
Examination
The “PECB Certified ISO 28000 Lead Implementer” exam fully meets the requirements of the PECB Examination and Certification Program (ECP). It covers the following competency domains:
- Domain 1: Fundamental principles and concepts of an SeMS
- Domain 2: Initiation of an SeMS implementation
- Domain 3: Planning of an SeMS implementation based on ISO 28000
- Domain 4: Implementation of an SeMS based on ISO 28000
- Domain 5: Evaluation of the performance of an SeMS based on ISO 28000
- Domain 6: Continual improvement of an SeMS based on ISO 28000
- Domain 7: Preparation for an SeMS certification audit
For specific information about exam type, languages available, and other details, please visit the List of PECB Exams and the Examination Rules and Policies.
Certification
After passing the exam, you can apply for one of the credentials shown in the table below. You will receive a certificate as soon as you fulfill all the requirements related to the selected credential.
For more information about the ISO 28000 certifications and the PECB certification process, please refer to the Certification Rules and Policies.
The table below presents the requirements for PECB ISO 28000 Implementer certifications:
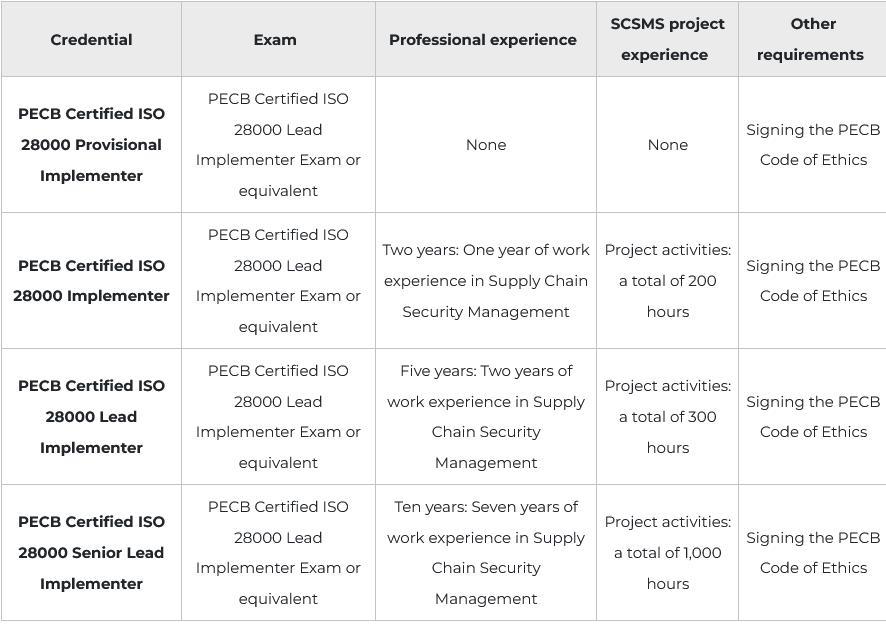
PECB Certified ISO 28000 Lead Implementer Supply Chain Security Management System Training Course
Note: PECB Certified Individuals who do possess the Lead Implementer and Lead Auditor Credentials are qualified for the respective PECB Master Credential, given they have taken 4 additional Foundation Exams which are related to this scheme. For more detailed information about the Foundation Exams and the overall Master Requirements, please go to PECB Master Credentials.
To be considered valid, the implementation activities should follow best implementation practices and include the following activities:
- Drafting an SeMS implementation plan
- Initiating an SeMS implementation project
- Managing or leading an SeMS implementation project
- Implementing an SeMS
- Managing documented information
- Evaluating the SeMS performance
- Performing continual improvement activities
What are the benefits of an effective SeMS based on ISO 28000?
A security management system based on ISO 28000 enables organizations to achieve their security management objectives. In particular, it enables organizations to:
- Enhance business capabilities
- Ensure the security of the environment in which they operate
- Comply with statutory, regulatory, and voluntary security obligations
- Identify and address risks and opportunities related to security management
- Effectively deal with security violations
- Recover from disruptions in the supply chain
- Manage relationships with all relevant interested parties in the supply chain
- Manage security-related risks
- Create and protect value
- Align security processes and controls with the organization’s objectives
- Gain a competitive advantage
For more information, visit the PECB PECB Certified ISO 28000 Lead Implementer | Supply Chain Security Management System course
Download the brochure PECB Certified ISO 28000 Lead Implementer | Supply Chain Security Management System course


